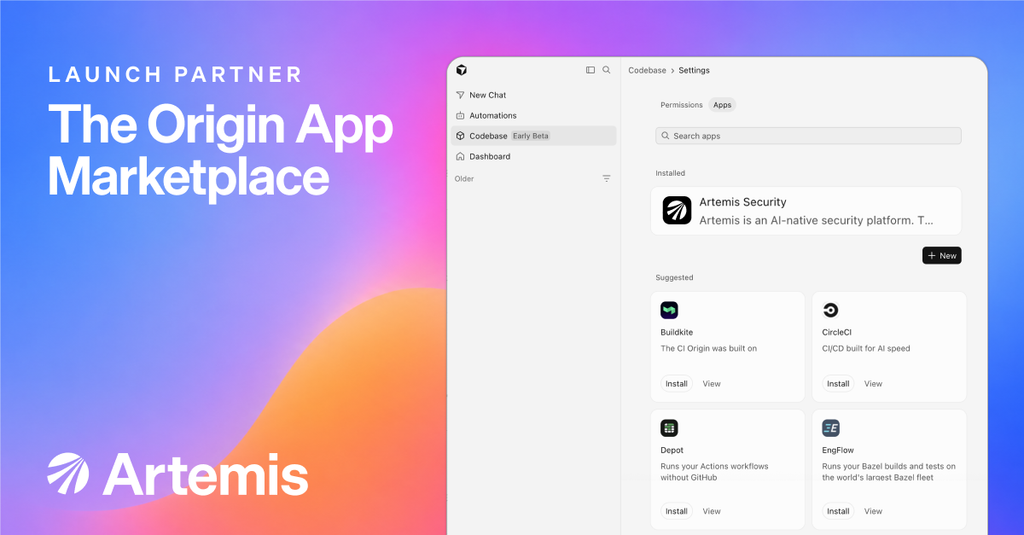
Artemis Security is a launch partner for the Cursor Origin App marketplace. Origin is Cursor’s new code hosting and git platform, and Artemis is one of 21 apps available at launch.
With Artemis, security teams that host code on Origin can detect suspicious and malicious activities associated with their Cursor and Origin usage. Artemis automatically analyzes code associated with potential security events with read-only access to the code behind an alert.
What the Artemis and Origin integration gives security teams
Detect suspicious activity across Cursor and Origin: Artemis integrates with Cursor’s audit logs. The Cursor Audit Logs connector brings in logins, member and role changes, API key and token activity, team and privacy settings, and Origin namespace, repository, and app-installation events. Artemis normalizes these events and runs detections over them alongside identity, cloud, endpoint, and SaaS activity from the rest of the environment. When a detection fires, the investigation ties back to the code through the Origin app.
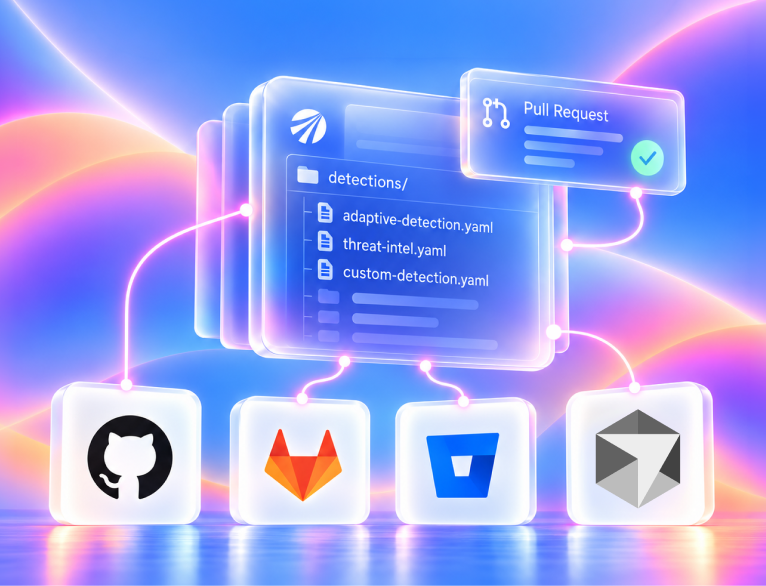
Analyze the code related to a potential incident: The Artemis app for Origin gives Artemis read-only access to the customer repositories in it: contents, metadata, pull requests, reviews, checks, and rulesets. The connection is federated so the code stays in Origin, and Artemis reads it only when an investigation needs it. Artemis’s AI agents read the code to investigate findings with full context, and analysts can open the repositories involved from AI Mode, directly inside the case.
How Cursor runs security operations on Artemis
Cursor is also an Artemis customer. One of the fastest-growing software companies of all time, Cursor replaced its legacy SIEM with Artemis and standardized on it for detection, investigation, and response across its environment.
Artemis correlates more than 35 of Cursor’s log sources and analyzes more than 1,000TB of security data a month. Every alert is investigated around the clock, and 96% of investigations are resolved autonomously, with the evidence attached. Instead of a static rule set, Artemis runs thousands of detectors tuned to Cursor’s environment and keeps tuning them as the environment changes. SpacexAI’s security engineers write custom detectors in plain language through AI Mode and the Artemis MCP server, work from Slack, and run threat hunts on new threat intelligence across the whole environment.
Getting started
Artemis customers can find the app under the Security Category in Origin’s app settings. Installing goes straight to the Artemis portal and creates the Origin connector, with no new account or separate setup. Teams can also start from Artemis, using Install on Origin on the connector’s setup page. To add detection, teams can connect Cursor Audit Logs.
Setup takes a namespace admin about two minutes. The app lives on the customer’s namespace, so there is no personal access token to create or rotate, and admins choose which repositories Artemis can read. Access is read-only.
Teams not yet using Artemis can book a demo to see the integration in action.